


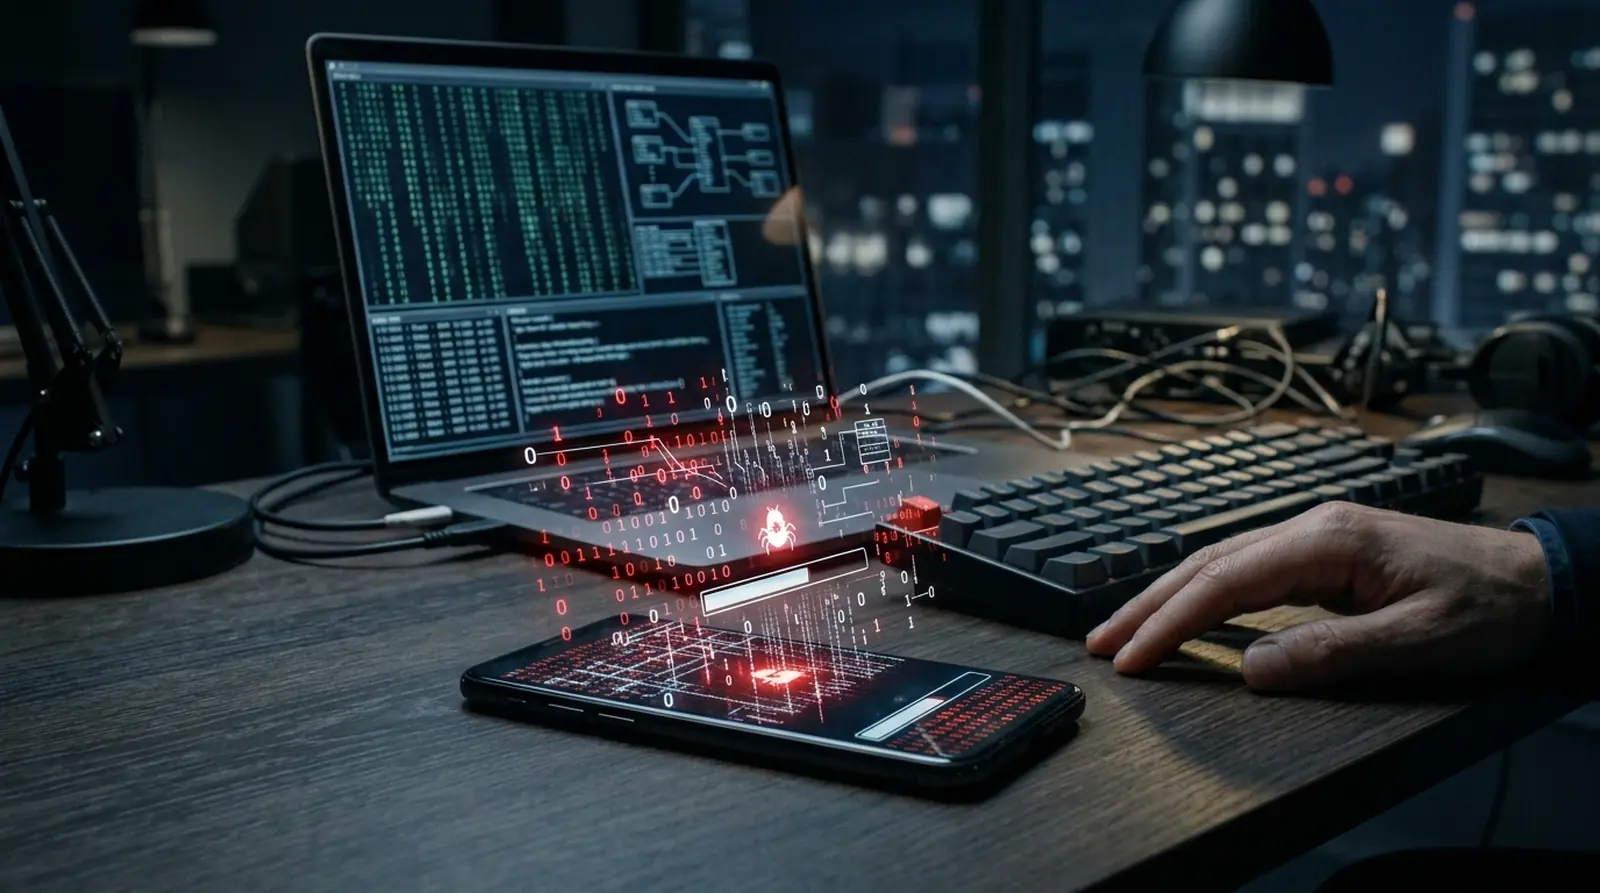
You probably scroll past ads without giving them much thought. But zero-click spyware ads can put a selected device at risk without you tapping anything, according to investigations published by Citizen Lab and Confiant. Researchers confirmed compromises involving 45 Al Jazeera Windows computers, while the advertising operation reached far beyond those targets.
Does that mean every ad on your phone is dangerous? Most people are unlikely to face this kind of targeted spyware attack, though the reports describe much wider tracking activity. Updates, ad blockers and built-in protection modes can help reduce your risk, with some limits.
| Detail | What we know |
|---|---|
| Report name | AdFection, Citizen Lab’s report number 195 |
| Published | October 15, 2026 |
| Ad firm | An Israeli advertising technology company |
| Spyware linked | Candiru, renamed Integrity Labs |
| Confirmed victims | 45 Al Jazeera Windows computers during 2024 and 2025 |
| Reach | 120,768 websites and 75,373 apps during March through June 2026 |
| Status | Google, IAB Europe and Beeswax removed the company’s access or listing |
What Happened With the AdFection Spyware Ads
You see, the company behind this operation had spent years inside the advertising system. Registered in Israel in March 2020, it remained on IAB Europe’s approved list and Google’s certified vendor lists until early October 2026. To understand how advertising became a route for spyware, here are the organizations named in the research.
- The ad firm. It operated MyDSP for buying advertising space and Controlium for selecting devices through advertising identifiers, browser cookies or IP addresses.
- Candiru. Citizen Lab identified the spyware vendor as a customer and assessed with high confidence that it was responsible for the Al Jazeera infections.
- Bindecy. Researchers linked this Israeli hacking business to the platform.
- Intelos. The reports connected this advertising intelligence company with location surveillance and spyware delivered through ads.
- Confiant. Its investigation examined suspicious advertising between April and September 2026, including code that collected cookies.
- Citizen Lab. Its researchers used network records supplied by Al Jazeera to confirm the compromises.
The confirmed newsroom attacks happened during 2024 and 2025. Researchers later examined billions of advertising bids from 2026, before major advertising businesses cut access in October. Both investigations became public on October 15, but Citizen Lab could not identify the government or customer that commissioned the attacks.
How Zero-Click Spyware Ads Reach a Device
You do not have to fall for a convincing message or press a suspicious button. According to Citizen Lab, an ad loading inside your browser or an app could begin the process, sometimes outside the area you could see. Here is the sequence researchers described.
- An advertiser buys the opening. The company wins an automated auction for advertising space. Its ad can then load on your device.
- Hidden code sends identifiers. A script passes information such as your advertising identifier, browser cookie identifier and IP address to a server. Those details help the operator distinguish devices.
- The server checks the target list. The system compares the incoming information with devices selected for attention. Controlium supported several ways to make that selection.
- Selected devices receive attack code. According to the report, the server sends malicious instructions only when it recognizes a chosen target. Other devices receive an empty response.
- Routine checks miss the harmful response. Advertising networks inspecting the ad may receive nothing dangerous themselves. That selective delivery helped the operation escape detection.
Confiant also found an encrypted connection that let operators send further code through an ad. However, it did not obtain the complete sequence of exploits, so its findings should not be read as proof that every suspicious ad caused an infection.
Who Was Targeted and How Far the Ads Spread
The numbers can sound alarming when you first read them. But an ad appearing on a network, a person being tracked and a computer being compromised represent different findings. Here is how the reported evidence breaks down.
Journalists and Newsrooms
If you work in journalism, the strongest confirmed evidence concerns Al Jazeera. Forbes reported that 45 Windows computers were compromised during 2024 and 2025, although what the spyware did on those machines remains unclear.
Citizen Lab also identified suspicious advertising directed toward journalists at as many as 18 additional outlets. Those findings were still being investigated, rather than counted as confirmed infections. Candiru had previously been linked to a 2021 attack involving Middle East Eye.
Governments and Sensitive Networks
You may have seen references to NATO, the UN, EU institutions, the Pentagon, the International Atomic Energy Agency and the International Criminal Court. Researchers reported advertising impressions on networks associated with those organizations, alongside semiconductor and defense businesses.
That tells you where ads appeared, not whether those organizations suffered spyware infections. The same distinction applies to named chip companies, including Nvidia, Broadcom and Micron.
Everyday Users and Mass Tracking
Your chances of encountering the advertising were much greater than your chances of being selected for spyware. Confiant estimated around 10 million impressions daily across 228 countries, and reported cookie collection involving more than 1,000 publisher websites.
Some collected cookies contained session identifiers or personal information. Confiant suggested that cookie matching could have subjected hundreds of millions of people to tracking, while saying only a very small proportion of ads delivered spyware.
Should Regular Phone Users Be Worried
You have reason to take the findings seriously without assuming your phone is infected. Citizen Lab describes selective spyware delivery alongside much wider collection of identifying information. Your personal risk depends partly on whether someone has a reason to target you.
If you are a journalist, activist, official, or work in defense or semiconductor businesses, the targeted activity deserves closer attention. Apple says most people will never face advanced spyware aimed specifically at them, and reserves Lockdown Mode for people at particular personal risk.
One detail matters before you draw conclusions about your phone. The confirmed Al Jazeera infections involved Windows computers, even though mobile apps accounted for most of the advertising bids examined. You should treat mobile advertising exposure as evidence of reach, while keeping confirmed computer infections separate from claims about phone compromises.
How to Protect Yourself From Zero-Click Spyware
You cannot judge an ad’s safety by how ordinary it looks. You can, however, reduce some routes attackers use to reach your device, starting with these habits and protection options.
Install Updates Right Away
Install operating system and browser updates when they become available, rather than leaving them waiting. Apple recommends current software for people facing spyware threats, though an updated device should never be treated as immune to every attack. This month’s October 2026 Patch Tuesday fixes are a good example of why Windows users should update too.
Turn On Lockdown Mode on iPhone, iPad and Mac
On your iPhone or iPad, open Privacy & Security, select Lockdown Mode and follow the activation and restart instructions. On your Mac, find Lockdown Mode under Privacy & Security and enable it separately.
Apple reserves this option for people at personal risk from advanced spyware. It restricts certain browser functions, message attachments and incoming communications, so some everyday features will work differently.
Use Advanced Protection on Android
Find Advanced Protection through your phone’s Security & Privacy menu, then enable Device protection. Google requires a screen lock, and your phone may need to restart.
The feature restricts several Chrome technologies and prevents certain security protections from being disabled. You can also enable Intrusion Logging, which preserves encrypted records that may help specialists investigate suspected interference.
Block Ads in Your Browser
Use an ad blocker to reduce the advertising content your browser loads. Citizen Lab’s Wolfie Christl told Forbes that blocking ads deserves a place among routine cybersecurity habits.
Still, do not treat it as complete protection. Christl also warned that defending reliably against malicious advertising is difficult.
Limit or Delete Your Advertising ID
On your iPhone, open Privacy & Security, choose Tracking and disable permission for apps to request tracking. Apple says this prevents apps from accessing your advertising identifier.
On Android 12 or later, look under Privacy, then Ads, for the option to delete that identifier. You will still receive ads, and targeting through cookies or your IP address remains possible.
Restart Your Phone Every Week
Follow the NSA’s advice to power your phone off and back on at least weekly. A restart may interrupt some malicious activity held in memory, but it cannot resolve every spyware infection or replace software updates.
Signs You May Have Been Targeted
You should take an official threat warning seriously, even if your phone seems normal. These are the alerts, specialist checks and next steps worth knowing about. For everyday warning signs, see our guide on how to know if your phone is hacked.
Apple Threat Notifications
Apple displays spyware warnings on your account page and also contacts affected users through email and iMessage. According to Apple, these notifications have reached people in more than 150 countries since 2021.
If you receive one, sign in directly to your Apple account website to check for the warning. Apple keeps its detection methods private to avoid helping attackers evade them.
Checking a Device With Amnesty’s MVT
Amnesty International’s Mobile Verification Toolkit examines iPhone backups and Android data for recognized spyware indicators. It is free, but its command-line workflow is intended for technical investigators rather than casual checks.
What to Do After a Warning
You do not have to work through a warning alone. Use these actions to reduce exposure and get qualified help.
| Step | Why it helps |
|---|---|
| Enable Lockdown Mode | Restricts features that advanced attacks may misuse |
| Install available updates | Brings your device’s software protections up to date |
| Contact a digital security group | Gives you access to specialist investigation |
| Move sensitive work to a clean device | Lets you continue important tasks away from the suspected device |
How Google and the Ad Industry Responded
You might expect vendor approval to catch this kind of activity. Yet Citizen Lab says the company remained listed for roughly six years before these responses.
- Google. Ended advertising platform access and added Chrome Safe Browsing alerts for associated websites.
- IAB Europe. Removed the company from its approved vendor register.
- Beeswax. Removed the company from its platform.
- Vungle. Suspended access while reviewing the matter.
- Eskimi. Blocked the company’s accounts.
Why Online Ads Are Now a Security Problem
You usually encounter advertising as a sales pitch, but its data and delivery systems can serve surveillance too. ADINT, or advertising intelligence, means using that infrastructure to identify, follow or reach people, which explains the calls for action.
Citizen Lab urged regulators to examine whether the ad company and Candiru violated laws. Confiant called for advertising businesses to give surveillance threats more attention, while earlier Pentagon warnings described troops being tracked through advertising and location data.
Where This Leaves Everyday Users
You do not need to assume every ad has compromised your device. The reports describe selective spyware attacks alongside tracking that reached far more people, so start with a few practical actions. Scam links in your inbox are still the more common threat, so keep our phishing email examples handy as well.
- Install outstanding device and browser updates.
- Add browser ad blocking to your security habits.
- Consider stronger built-in protection if your work or circumstances make you a likely target.
Keep those habits going, and take any official threat notification seriously. If one arrives, get specialist help before returning to sensitive work.
FAQs
Zero-click spyware can compromise your device without requiring you to press a link, open a file or approve an installation. In the AdFection operation, Citizen Lab described advertising code that checked whether your device had been selected before sending attack instructions.
Yes, advertising can provide a route for an attack that requires no tap from you. However, the verified Al Jazeera compromises involved Windows PCs, so you should not interpret the reported mobile advertising totals as a count of infected phones.
An ad blocker can reduce your exposure, but you cannot count on it to prevent every advertising-based attack. Keep your browser updated too, and consider stronger device protections if you face a particular threat.
You may receive an official threat notification or need a specialist to examine your device for evidence. Apple sends targeted attack alerts, while Android’s optional Intrusion Logging can preserve useful investigative records. Amnesty’s MVT can assist a technical examination, though it is unsuitable as a simple home check.
You generally have less reason to enable Lockdown Mode unless your circumstances make targeted spyware a credible concern. Apple designed it for a small group facing exceptional threats, and its restrictions can affect websites, attachments and calls.
You can install updates, enable Advanced Protection where available and block browser advertising. Deleting your advertising identifier removes one means of selecting your device, though cookies and IP addresses remain usable. A weekly restart may help against some attacks, but it is no guarantee.
